
What Are Network Security Risks?
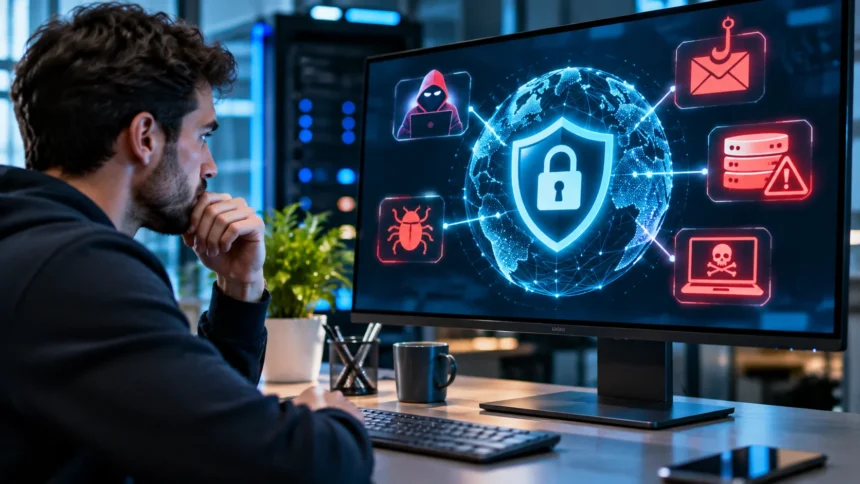
Network security risks are potential threats and weaknesses that can compromise computer networks, connected devices, and sensitive information. These risks arise from cyberattacks, software vulnerabilities, human mistakes, and improper security configurations. Businesses rely on networks to communicate, store information, and manage operations. Understanding network security risks helps organizations identify weaknesses before they lead to serious problems.
Modern networks connect computers, mobile devices, cloud platforms, servers, and business applications. Every connection introduces responsibilities for protecting information and controlling access. When appropriate safeguards are missing, unauthorized individuals may gain access to valuable systems. These incidents can interrupt operations, expose confidential records, or create financial losses for businesses and their customers.
Network security is not limited to installing antivirus software or configuring a firewall. Effective protection requires identifying important assets, understanding possible threats, and applying suitable controls. Employees, administrators, and business leaders all have responsibilities. A practical approach combines secure technology, ongoing monitoring, employee education, and preparation for unexpected security incidents.
Why Network Security Risks Matter for Businesses
Businesses depend on computer networks for daily operations, including customer communication, payment processing, and information management. A security incident can interrupt these activities and reduce productivity. Even a temporary outage may affect customer service or important business deadlines. Understanding potential threats helps organizations prepare for disruptions and maintain more reliable operations.
Financial consequences are another major concern. Cybersecurity incidents may involve recovery expenses, service interruptions, legal obligations, and investigation costs. Organizations may also experience reputational damage when sensitive customer information becomes exposed. The total impact depends on the nature of the incident, the affected systems, and the organization’s ability to respond.
Strong network protection also supports customer confidence and regulatory compliance. Many businesses handle personal information that requires appropriate safeguards. Failing to protect this information can create privacy concerns and legal consequences. Regular risk assessments, security policies, and employee awareness help organizations reduce exposure while supporting responsible business practices.
Malware and Ransomware Attacks
Malware is malicious software designed to interfere with computer systems, access information, or perform unauthorized activities. Common categories include viruses, worms, trojans, and spyware. These threats may affect individual computers or larger business networks. Malware infections can disrupt normal operations, damage files, or expose sensitive information without the knowledge of authorized users.
Ransomware is a particularly disruptive form of malware that can encrypt files or otherwise make systems unavailable. Some ransomware incidents also involve threats to disclose stolen information. Organizations may experience prolonged operational interruptions and expensive recovery procedures. Paying a ransom does not guarantee that files will be restored or that stolen information will remain private.
Businesses can reduce malware risks through regular software updates, reputable endpoint protection, and appropriate network segmentation. Secure backups are especially important for recovering from ransomware incidents. Employees should also understand the risks of suspicious downloads and unexpected attachments. Combining several defensive measures provides stronger protection than relying on one security product.
Phishing and Social Engineering Threats
Phishing is a common cybersecurity threat that uses deceptive communication to obtain information or influence someone into performing an unsafe action. Attackers may impersonate employers, financial institutions, or familiar service providers. These messages often appear through email, text, or online communication platforms. Their success depends heavily on manipulating trust and creating convincing situations.
Social engineering attacks can create serious network security risks even when technical defenses are strong. An employee might receive a fraudulent request that appears to come from a manager or trusted colleague. The attacker may use urgency to discourage verification. Such incidents demonstrate that cybersecurity involves human decisions as well as technology.
Organizations should train employees to recognize suspicious requests and verify sensitive instructions through trusted communication channels. Multifactor authentication can reduce the impact of stolen passwords. Email filtering and appropriate reporting procedures provide additional safeguards. A supportive reporting culture encourages employees to raise concerns before a suspicious message causes harm.
Weak Passwords and Unauthorized Network Access
Weak passwords are a common source of account security problems. Simple or reused credentials may allow unauthorized users to access business systems when passwords become exposed. Attackers can obtain login information through phishing, data breaches, or other compromises. Once an account is accessed, connected resources may also become vulnerable.
Password-related risks increase when employees use the same credentials across several applications. Administrative accounts present additional concerns because they often have broader permissions. Inactive accounts and unnecessary access privileges can create weaknesses that remain unnoticed. Managing identities carefully is therefore an essential component of protecting business networks.
Organizations should encourage unique passwords and use appropriate password managers. Multifactor authentication adds another layer of protection, with phishing-resistant methods preferred when available. Access permissions should follow the principle of least privilege. Regular account reviews can identify unused credentials and reduce unnecessary access to sensitive systems.
Insider Threats and Employee Mistakes
Insider threats are network security risks associated with people who already have authorized access to organizational systems. These individuals may include employees, contractors, or business partners. Insider incidents can result from deliberate actions or accidental mistakes. Understanding both possibilities helps businesses design security measures that protect information without assuming every employee is untrustworthy.
Human error can involve sending confidential documents to the wrong recipient, changing security settings incorrectly, or sharing sensitive information. These mistakes may create vulnerabilities even when no malicious intent exists. Deliberate misuse of access can cause additional harm. Organizations should address both categories through appropriate policies, training, and technical safeguards.
Access restrictions and regular permission reviews help limit the potential impact of insider incidents. Clear procedures for handling sensitive information can reduce accidental exposure. Monitoring should remain proportionate and respect applicable privacy requirements. Encouraging employees to report mistakes promptly also helps security teams respond before problems become more serious.
Cloud Security Risks and Misconfigurations
Cloud computing allows organizations to store information and operate applications through externally managed infrastructure. Although cloud providers offer security capabilities, customers remain responsible for many account, application, and configuration decisions. Incorrect settings can expose sensitive resources. Understanding the shared responsibility model is essential for managing cloud network security risks.
Common cloud security concerns include excessive permissions, publicly accessible storage, and poorly protected service accounts. Organizations using multiple cloud platforms may struggle to maintain consistent security settings. Rapid application development can also introduce overlooked configurations. Without suitable oversight, vulnerabilities may remain unnoticed until they cause a security incident.
Businesses should regularly review cloud access permissions, network configurations, and data protection controls. Encryption and centralized monitoring may reduce exposure when implemented appropriately. Cloud security posture management tools can help identify some configuration weaknesses. Clear documentation of responsibilities supports more consistent protection across different services and teams.
Unsecured Wi-Fi and Remote Work Connections
Wireless networks provide convenient connectivity for employees, customers, and visitors. However, outdated security settings or weak authentication may expose connected devices to unauthorized access. Public networks can also introduce risks when users connect without appropriate protections. Businesses should understand how wireless access affects the security of internal applications and sensitive information.
Remote working arrangements create additional challenges because employees may connect through home networks or personal devices. These environments are not always managed by organizational IT teams. Outdated software, insecure equipment, or compromised accounts can increase exposure. Allowing broad internal access through remote connections may create unnecessary risks.
Secure remote access solutions can help protect business resources. Depending on organizational needs, these may include VPNs, Zero Trust Network Access, and managed devices. Strong authentication and regular software updates provide additional safeguards. Separating guest wireless networks from sensitive business infrastructure also reduces the consequences of unauthorized connections.
Data Breaches and Sensitive Information Exposure
A data breach occurs when confidential information is accessed, disclosed, altered, or lost without authorization. Businesses may store customer records, financial information, employee details, and proprietary documents. Unauthorized exposure can create privacy concerns and operational difficulties. The seriousness of a breach depends on the information involved and the circumstances surrounding the incident.
Data breaches may result from stolen credentials, software vulnerabilities, configuration errors, or compromised third-party systems. Accidental disclosures can also expose valuable information. In some cases, an organization may not recognize the incident immediately. Appropriate monitoring and incident detection procedures help reduce delays in identifying possible exposure.
Organizations should classify sensitive information and restrict access according to business needs. Encryption, secure storage, and appropriate data retention policies can reduce certain risks. Incident response plans should explain how suspected breaches are investigated and reported. Legal notification requirements vary, making preparation and professional guidance important.
Outdated Software and Unpatched Vulnerabilities
Outdated software can expose business networks to known security weaknesses. When developers discover vulnerabilities, they may release updates that correct the problem. Organizations that delay necessary updates may remain exposed to preventable threats. Unsupported applications and operating systems can create additional concerns because security fixes may no longer be available.
Patch management becomes more challenging when a company operates many different devices and applications. Updates may require testing to avoid compatibility problems or operational interruptions. Older business systems can be particularly difficult to maintain. Without an organized process, important vulnerabilities may remain unresolved across multiple areas of the network.
A practical patch management program begins with maintaining an accurate technology inventory. Security teams should prioritize vulnerabilities according to severity, exploitation evidence, and business impact. Unsupported systems may need replacement or additional protective controls. Regular maintenance helps reduce exposure while supporting dependable network operations.
Distributed Denial-of-Service Attacks
Distributed denial-of-service attacks attempt to overwhelm online services or network infrastructure with excessive traffic or requests. These incidents can prevent legitimate users from accessing websites, applications, or other digital services. Businesses that depend on continuous internet availability may experience substantial disruption. The impact can affect customers, employees, and connected operations.
DDoS attacks differ from many other security incidents because their primary objective is often service disruption rather than information theft. However, they can occur alongside other malicious activities. The volume and characteristics of traffic vary between incidents. This makes effective detection and response planning especially important for public-facing systems.
Organizations can improve resilience through traffic filtering, specialized mitigation services, and appropriate infrastructure design. Content delivery networks may help distribute some forms of traffic. Coordination with internet service providers is also valuable. A tested response plan can reduce confusion when unexpected traffic prevents customers from reaching important services.
Internet of Things and Connected Device Risks
Internet of Things devices include network-connected cameras, printers, sensors, and building management equipment. These systems can improve operational efficiency, but they also introduce security responsibilities. Some devices have limited protective features or receive infrequent updates. Each additional connection can expand the organization’s potential attack surface.
IoT security problems may involve default passwords, unnecessary services, or outdated firmware. Certain devices cannot support conventional endpoint protection tools. Businesses may also have difficulty identifying every connected device. Poor visibility makes it harder to recognize vulnerabilities and determine which systems require maintenance or additional safeguards.
Organizations should maintain an inventory of connected equipment and apply appropriate configuration standards. Changing insecure default credentials and installing supported updates can reduce exposure. Network segmentation helps restrict communication between IoT devices and critical business systems. Purchasing equipment from vendors with dependable security support can improve long-term management.
Third-Party Vendors and Supply Chain Risks
Many businesses rely on external providers for software, cloud hosting, payment processing, and technical support. These relationships provide valuable services but may create additional network security risks. A compromised vendor can potentially affect organizations that depend on its systems. Managing third-party access is therefore an important part of cybersecurity planning.
Vendor risks can arise from insecure software, excessive account permissions, or inadequate information protection practices. Organizations may have limited visibility into how external providers maintain their infrastructure. Contractual responsibilities can also become unclear. Businesses should evaluate these concerns before granting access to sensitive systems or information.
A third-party risk management process should consider vendor security practices, data handling responsibilities, and incident notification procedures. External accounts should receive only necessary permissions. Important relationships may require periodic reviews. Clear communication and documented expectations can help organizations reduce dependencies that might otherwise create unexpected security problems.
Poor Security Monitoring and Incident Response
Organizations may struggle to identify cyber threats when they lack visibility into network activity. Security logs, device alerts, and access records can provide useful information about suspicious events. However, collecting information alone does not guarantee effective detection. Teams need processes for reviewing relevant alerts and distinguishing important threats from routine activity.
Slow incident response can increase the impact of an attack. Employees may be uncertain about reporting suspicious behavior, while technical teams may lack clear responsibilities. Communication problems can delay containment and recovery. These challenges become more serious when critical applications or sensitive customer information are affected.
Businesses should develop incident response plans that define reporting procedures, responsibilities, and communication channels. Regular exercises help identify weaknesses before real incidents occur. Centralized monitoring tools may support faster detection when properly configured. Reviewing previous incidents can also improve future response procedures and strengthen overall network resilience.
How to Identify and Assess Network Security Risks
A network security risk assessment helps organizations understand which threats could affect their systems and operations. The process begins with identifying important assets, including devices, applications, information, and connections. Businesses then consider possible vulnerabilities and threat scenarios. This provides a structured foundation for deciding which protections deserve priority.
Risk evaluation usually considers the likelihood of a threat and its potential impact. For example, exposure involving customer financial information may require greater attention than a less critical internal system. However, assessments should reflect actual business circumstances. A risk that is significant for one organization may be less important for another.
Security assessments should be repeated when technology or business operations change. New applications, employees, and external services can introduce additional vulnerabilities. Documentation helps teams track identified risks and planned improvements. Regular reviews also support accountability and make cybersecurity investment decisions easier to explain.
Best Practices for Reducing Network Security Risks
Reducing network security risks requires a combination of preventive measures and ongoing management. Strong authentication, timely software updates, secure configurations, and endpoint protection address several common weaknesses. Network segmentation can also limit unnecessary communication between systems. These controls provide layers of defense rather than depending entirely on one security technology.
Employee education is equally important because many incidents involve deceptive messages or accidental mistakes. Clear policies help employees recognize their responsibilities. Regular security awareness activities can reinforce appropriate behavior. Organizations should also provide convenient reporting methods so suspicious incidents can be investigated without unnecessary delays.
Reliable backups, incident response planning, and continuous monitoring support recovery when preventive controls are insufficient. Security responsibilities should be clearly assigned and reviewed regularly. Businesses may benefit from professional assessments when internal expertise is limited. Effective protection focuses on meaningful risk reduction and continuous improvement rather than assuming every possible threat can be eliminated.
Conclusion
Network security risks include malware, phishing, stolen credentials, cloud misconfigurations, data breaches, and insecure connected devices. These threats can interrupt business activities, expose sensitive information, and create financial consequences. Understanding common vulnerabilities helps organizations evaluate their security needs. A clear risk management strategy provides the foundation for more dependable network protection.
Businesses can reduce exposure through strong authentication, regular updates, access restrictions, employee training, and security monitoring. Incident response planning and reliable backups are also important. No individual technology can prevent every possible cyberattack. Combining multiple safeguards creates a more resilient security environment that can adapt to changing threats.
Managing network security is an ongoing responsibility that requires attention from technical teams and organizational leaders. Regular assessments help identify new weaknesses as systems evolve. Clear procedures and appropriate investments support long-term protection. By understanding network security risks and addressing them proactively, businesses can improve operational reliability and protect valuable information.
Frequently Asked Questions
What are the most common network security risks?
Common risks include malware, ransomware, phishing, weak passwords, unauthorized access, outdated software, and cloud misconfigurations. These threats can compromise sensitive information or disrupt important business services.
Why are network security risks increasing?
Cloud adoption, remote work, connected devices, and complex digital systems create more potential vulnerabilities. Attackers also adapt their methods, making continuous monitoring and updated security practices important.
How can businesses reduce network security risks?
Businesses can implement multifactor authentication, regular security updates, network segmentation, endpoint protection, employee training, and reliable backups. Regular assessments help identify weaknesses requiring additional attention.
What is the biggest risk to network security?
There is no single biggest risk for every organization. Compromised credentials, phishing, and unpatched vulnerabilities are significant concerns, but priorities depend on business systems and threat exposure.
What is a network security risk assessment?
A network security risk assessment identifies important systems, potential threats, and vulnerabilities. It evaluates possible consequences and helps organizations prioritize appropriate safeguards and security improvements.