
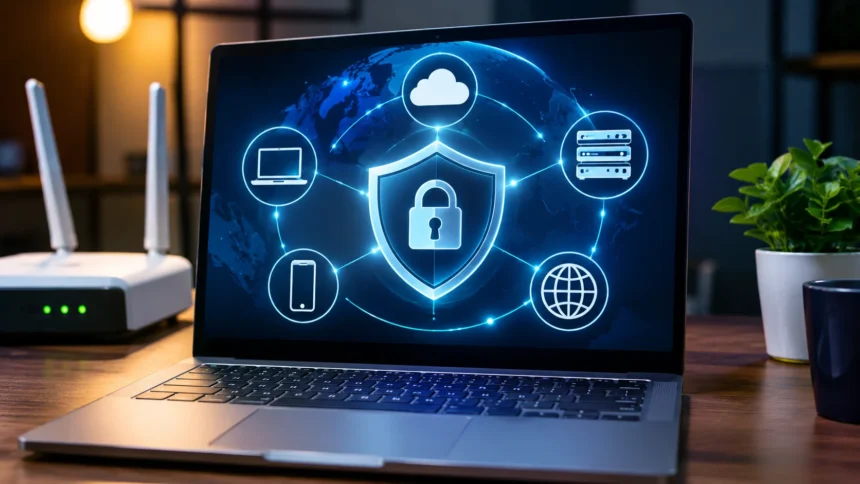
Network security protects the devices, information, and systems connected through a computer network. It helps prevent unauthorized access, data theft, and other online threats that can disrupt everyday activities. Whether you are browsing the internet at home or managing business information, network security plays an important role in keeping your digital environment safer.
Understanding how network security works does not have to be complicated. You do not need advanced technical knowledge to understand the basic tools and practices involved. This guide explains network security in simple words, including how it protects information, identifies threats, and helps individuals and businesses stay connected safely.
What Is Network Security in Simple Words?
Network security is the process of protecting computers, devices, and information that communicate through a network. It involves using tools, settings, and safety practices to prevent unauthorized people from accessing important resources. A secure network allows approved users to exchange information while reducing the risks associated with online threats.
Think of network security like protecting a building with several security measures. Doors control entry, identification checks confirm visitors, and cameras help detect unusual activity. Similarly, network security tools control digital connections, verify users, and monitor suspicious behavior to help protect computers and valuable information.
Network security is important for homes, schools, offices, and large organizations. Every connected device may contain information that needs protection, including personal details, passwords, and confidential files. By combining reliable security tools with responsible online habits, users can reduce the likelihood of unwanted access and other cybersecurity problems.
How Does Network Security Work?
Network security works by checking connections, controlling access, and monitoring activity across connected devices. Different security technologies examine information entering or leaving a network to identify potential risks. When a connection violates established security rules, protective systems may block it or alert administrators about the suspicious activity.
For example, imagine someone trying to connect to a company’s private network without permission. Access controls can require the person to verify their identity before allowing entry. If the request appears unauthorized, the system may deny access, helping prevent sensitive business information from being exposed to unknown users.
Network security also uses several protective layers rather than depending on one tool. Firewalls, encryption, authentication systems, and monitoring software perform different tasks. Working together, these measures help protect information, support reliable communication, and reduce the impact of certain cyberattacks when individual security controls fail.
Why Is Network Security Important?
Network security matters because people regularly share valuable information through internet-connected devices. Online banking, business communication, school platforms, and cloud storage all depend on networks. Without appropriate protection, attackers may attempt to steal passwords, access private documents, or interfere with services that individuals and organizations rely on daily.
Businesses also depend on secure networks to maintain normal operations. A successful cyberattack can interrupt communication, prevent access to essential files, and create unexpected recovery expenses. Strong security measures help organizations lower these risks while supporting employees who need reliable access to applications, information, and connected systems.
Another important reason is maintaining privacy and trust. Customers expect companies to handle personal information responsibly, while employees need confidence that workplace systems are properly protected. Network security supports these expectations by controlling access, protecting sensitive communications, and helping organizations identify problems before they cause widespread disruption.
The Three Main Goals of Network Security
Network security focuses on three important goals: confidentiality, integrity, and availability. These principles explain what security measures are designed to protect and why different technologies are necessary. Together, they help organizations create environments where information remains private, accurate, and accessible to people who have permission to use it.
Confidentiality means keeping sensitive information away from unauthorized individuals. Integrity ensures that information remains accurate and is not changed without permission. For example, an employee should be able to view an approved financial report without worrying that someone secretly modified important figures or accessed confidential information.
Availability means making sure systems and information remain accessible when legitimate users need them. A secure network should protect resources without unnecessarily preventing everyday activities. Reliable backups, system maintenance, and protection against disruptive attacks all contribute to availability by helping organizations maintain essential services during unexpected problems.
How Firewalls Protect a Network
A firewall is a security tool that helps control information moving into and out of a network. It examines network connections and compares them with established security rules. Depending on those rules, the firewall can allow appropriate communication or block traffic that may create unnecessary security risks.
Think of a firewall as a security checkpoint at the entrance to a building. Visitors must satisfy certain entry requirements before gaining access to protected areas. In a similar way, firewalls evaluate network communication and determine whether connections should be permitted based on their settings and available information.
Firewalls are used in home routers, office networks, individual computers, and cloud environments. Some provide basic connection filtering, while more advanced systems can examine application traffic and identify suspicious patterns. However, a firewall cannot prevent every online threat, so it should work alongside other security technologies and safe user practices.
How Passwords and Authentication Keep Networks Safe
Passwords help prevent unauthorized users from accessing accounts, devices, and network resources. When someone attempts to sign in, the system checks whether the submitted credentials meet its authentication requirements. Strong, unique passwords make it harder for attackers to gain access through common guessing techniques or previously exposed account credentials.
Authentication can also involve additional verification methods beyond a password. Multifactor authentication may require a security key, authentication application, or another approved verification step. This extra protection helps reduce account takeover risks because knowing a password alone may not be enough to complete the login process.
Access control works closely with authentication by deciding what verified users are allowed to do. For example, a company employee may access shared documents without receiving permission to modify network settings. Limiting access according to responsibilities helps protect sensitive information and reduces the potential consequences of compromised accounts.
How Encryption Protects Your Information
Encryption protects information by converting readable data into a format that unauthorized people cannot easily understand. The original information can be restored using the appropriate decryption key. This technology helps protect sensitive details when they travel between devices or remain stored on computers, servers, and other systems.
For example, secure websites commonly use encrypted connections to protect information exchanged between browsers and web servers. This helps prevent others on the communication path from reading protected content. Encryption is particularly useful when accessing accounts, sending confidential documents, or using online services over networks that may not be fully trusted.
However, encryption does not solve every security problem. It cannot automatically prevent someone from stealing information after gaining legitimate account access or compromising an unlocked device. For effective protection, encryption should be combined with strong authentication, secure software, careful access management, and other essential cybersecurity practices.
How Network Security Detects Suspicious Activity
Network security tools help identify unusual behavior by monitoring connections, devices, and system activity. They may record login attempts, unexpected traffic patterns, and communication with unfamiliar services. Security teams review this information to determine whether an event represents normal activity, a technical problem, or a possible cybersecurity threat.
Intrusion detection systems are designed to recognize certain suspicious activities and generate alerts. These tools may compare network behavior against known attack patterns or identify unexpected changes. An alert does not always mean an attack has occurred, but it provides useful information for further investigation and security decisions.
Intrusion prevention systems can go a step further by automatically blocking some potentially harmful activity. For example, they may stop traffic that matches established malicious patterns. Although these systems help reduce risks, they require proper configuration and ongoing review because legitimate activity can sometimes resemble suspicious behavior.
How Network Security Prevents Malware Attacks
Malware refers to harmful software designed to steal information, damage systems, or interfere with normal operations. Common examples include viruses, spyware, worms, and ransomware. Malware may enter networks through unsafe downloads, malicious attachments, compromised applications, or devices that contain unpatched software vulnerabilities.
Network security reduces malware risks by combining several protective measures. Firewalls can restrict certain unwanted connections, while endpoint protection software examines suspicious files and activities on devices. Email filtering and website protection tools may also help identify harmful content before users accidentally interact with it.
Regular software updates are another important part of malware prevention. Developers release patches to address security weaknesses that attackers might exploit. Organizations should also maintain reliable backups and educate users about suspicious messages, reducing both the likelihood of successful infections and the potential damage caused by security incidents.
How Wi-Fi Network Security Works
Wi-Fi security protects wireless communication between devices and network equipment. Because wireless signals travel through the surrounding area, appropriate security settings are important. Modern Wi-Fi encryption helps prevent unauthorized individuals from easily reading information exchanged over a protected wireless connection.
Home networks typically use a router that manages connections between local devices and the internet. A strong Wi-Fi password helps prevent unwanted access, while router administration credentials protect important configuration settings. WPA3 provides modern wireless protection when supported, and WPA2-AES remains useful for compatible older equipment.
Keeping router firmware updated also helps protect against discovered security weaknesses. Users can improve protection by creating separate guest networks and reviewing connected devices periodically. These practices help reduce unnecessary access to household devices while allowing family members and approved visitors to use internet services more safely.
How Network Security Protects Small Businesses
Small businesses often manage customer information, business documents, payment records, and employee accounts through connected systems. These resources can attract attackers, even when an organization has relatively few employees. Appropriate network security helps protect sensitive information and supports dependable daily operations without requiring unnecessarily complex infrastructure.
A basic security approach may include firewalls, strong authentication, regular updates, and endpoint protection. Business owners should also control who can access financial records, administrative settings, and confidential documents. Limiting permissions helps prevent accidental exposure and reduces the amount of information available through a compromised employee account.
Employee training is another essential part of business network protection. Staff members should understand how to recognize suspicious emails, protect login credentials, and report possible security problems. Clear procedures, secure backups, and regular security reviews help smaller organizations respond more effectively when unexpected incidents affect their systems.
How Network Security Works in Cloud Computing
Cloud computing allows individuals and organizations to access applications, storage, and computing resources through internet-connected services. These environments use network security controls to help protect communication and restrict access to important resources. However, protecting cloud information requires cooperation between the service provider and the organization using the platform.
Cloud providers typically protect certain parts of the underlying infrastructure, while customers remain responsible for other security settings. Responsibilities vary depending on the type of cloud service. For example, customers may need to manage account permissions, protect confidential information, configure applications, and monitor activity within their cloud environments.
Cloud network security may involve encryption, firewalls, identity management, activity logging, and network access restrictions. These measures help control how users and applications communicate with protected resources. Regular configuration reviews are especially important because incorrect permissions or exposed credentials can create security problems even when the cloud provider maintains strong infrastructure protections.
How Network Security Supports Remote Work
Remote work allows employees to access business resources from homes, shared offices, and other locations. Although this flexibility offers practical benefits, it also creates additional security considerations. Organizations must protect information accessed outside traditional workplaces while ensuring employees can use necessary tools and communicate effectively.
Secure remote access systems help control connections between employees and company resources. Virtual private networks can provide encrypted communication paths, while identity-based access tools restrict connections according to approved permissions. Multifactor authentication adds another layer of protection when employees sign in to important applications and business systems.
Employees can support remote network security by keeping devices updated and following company access policies. They should also protect work accounts and avoid sharing sensitive information through unapproved services. Organizations benefit from providing clear instructions, appropriate security tools, and reliable support when workers encounter suspicious activity or technical problems.
Common Network Security Threats Explained Simply
Phishing is a common online threat that attempts to trick people into sharing sensitive information or performing unsafe actions. Attackers may create emails or messages that appear to come from trusted organizations. These messages sometimes contain misleading links that direct users toward fraudulent websites or attempt to collect account credentials.
Denial-of-service attacks are another type of network threat. Their purpose is to make online services unavailable by overwhelming systems or otherwise exhausting essential resources. Businesses may experience interrupted websites, unavailable applications, or reduced service performance when attackers successfully disrupt the systems supporting online communication.
Unauthorized access occurs when someone reaches a device, account, or network resource without appropriate permission. Attackers may exploit weak passwords, exposed credentials, or software vulnerabilities. Understanding these common threats helps individuals recognize why different security measures are necessary and why protecting networks involves more than installing one defensive application.
Simple Network Security Tips Anyone Can Follow
Using strong, unique passwords is one of the most practical ways to improve everyday network security. A password manager can help create and organize complex credentials without requiring users to memorize every password. Enabling multifactor authentication provides additional protection for important accounts, especially email, financial services, and administrative access.
Updating devices regularly is another simple but valuable security habit. Operating systems, browsers, applications, and routers may contain weaknesses that developers address through security patches. Automatic updates can help reduce delays, although organizations may need controlled testing before applying changes to important business systems.
Users should also be careful when downloading files or responding to unexpected requests. Verify unfamiliar messages through trusted channels before sharing private information or opening attachments. Regular backups and secure Wi-Fi settings provide additional protection, helping reduce the potential consequences of device failures, accidental mistakes, and certain cybersecurity incidents.
Common Network Security Mistakes to Avoid
A frequent mistake is assuming that a strong password alone provides complete protection. Passwords are important, but compromised devices and deceptive messages can create risks even when credentials are difficult to guess. Combining strong passwords with multifactor authentication and secure software provides a more dependable approach to account protection.
Another mistake is neglecting software updates or using outdated network equipment. Unsupported devices may no longer receive important security patches, leaving known vulnerabilities unresolved. Reviewing equipment regularly and replacing unsupported products when practical helps maintain protection against weaknesses that attackers may already understand.
Some users also overlook backups, monitoring, and incident response planning. Without these measures, recovering from a security problem may become more difficult. Maintaining protected backups, reviewing unusual activity, and knowing how to report incidents helps individuals and organizations respond more quickly when unexpected problems occur.
How to Create a Basic Network Security Plan
Creating a network security plan begins with identifying the devices, accounts, and information that need protection. This may include computers, smartphones, routers, business applications, and cloud storage. Understanding which resources are important makes it easier to select appropriate safeguards and identify areas where security improvements are most necessary.
Next, establish practical protection measures for everyday activities. Enable strong authentication, install necessary updates, configure network equipment securely, and review account permissions. Important files should have reliable backups, while sensitive information should be accessible only to people who need it for legitimate purposes.
Finally, review the security plan regularly and adjust it when technology or circumstances change. New devices, applications, employees, and online services may introduce additional risks. Ongoing maintenance, basic training, and occasional security checks help keep protective measures relevant without requiring unnecessary technical complexity.
The Future of Network Security
Network security continues to evolve as more devices and services connect to the internet. Cloud computing, remote work, and smart technology have expanded the number of systems that organizations need to protect. Security approaches must adapt to these changes while maintaining reliable access for legitimate users and applications.
One important development is zero trust security, which emphasizes verifying access rather than automatically trusting devices connected to an internal network. Users and systems receive access according to established identity and security requirements. This approach can reduce unnecessary permissions and limit potential exposure when attackers compromise individual accounts or devices.
Artificial intelligence and automated monitoring are also becoming important parts of cybersecurity operations. These technologies can help analyze large amounts of network activity and identify patterns that deserve investigation. However, effective protection still depends on reliable configurations, appropriate human oversight, regular maintenance, and responsible decisions about how security tools are used.
Conclusion
Understanding how network security works becomes easier when you focus on its main purpose: protecting connected devices, information, and communication. Firewalls control traffic, authentication checks identities, and encryption protects sensitive data. Together with monitoring and other protective measures, these technologies help reduce the risks associated with unauthorized access and cyberattacks.
You do not need to be a technical expert to apply basic network security practices. Strong passwords, multifactor authentication, software updates, secure Wi-Fi settings, and regular backups can make a meaningful difference. Businesses can strengthen these foundations through employee training, access management, monitoring, and clear security procedures.
Network security is not a one-time task because technology and online threats continue to change. Maintaining safe habits and reviewing protective measures regularly helps keep systems more dependable. By understanding the basics and taking practical steps, individuals and organizations can create safer digital environments without becoming overwhelmed by technical terminology.
Frequently Asked Questions (FAQs)
How Does Network Security Work in Simple Terms?
Network security works by controlling access, protecting information, and monitoring suspicious activity. Tools such as firewalls, authentication systems, and encryption help prevent unauthorized connections while allowing approved users to communicate safely.
What Is the Main Purpose of Network Security?
The main purpose of network security is to protect connected systems and information from unauthorized access, misuse, and disruption. It helps maintain privacy, preserve information accuracy, and support reliable access to essential services.
What Is a Real-Life Example of Network Security?
A home Wi-Fi router protected by strong encryption and a unique password is a simple example. These settings help prevent unauthorized connections and protect wireless communication between approved devices.
Is Network Security the Same as Cybersecurity?
No, network security is one part of cybersecurity. Network security focuses on connected devices, communication, and network infrastructure, while cybersecurity also covers applications, information, user identities, and other digital systems.
How Can Beginners Learn Network Security?
Beginners can start by understanding firewalls, passwords, encryption, and secure Wi-Fi settings. Learning safe browsing habits, practicing basic device protection, and exploring beginner-friendly networking concepts can gradually build useful knowledge.